According to Gartner, Endpoint Detection and Response (EDR) is defined as a solution that “records and stores endpoint-system-level behaviors, use various data analytics techniques to detect suspicious system behavior, provide contextual information, block malicious activity, and provide remediation suggestions to restore affected systems.”
A true EDR tool should have the following capabilities:
- Incident data search and investigation
- Alert triage or suspicious activity validation
- Suspicious activity detection
- Threat hunting or data exploration
- Stopping malicious activity
What is the difference between EDR and Antivirus? Antivirus is the prevention component of endpoint security, which aims to stop cyber threats from entering a network. When threats slip past an antivirus, EDR detects that activity and allows teams to contain the adversary before they can move laterally in the network.
Posted from: https://www.crowdstrike.com/cybersecurity-101/endpoint-security/endpoint-detection-and-response-edr/
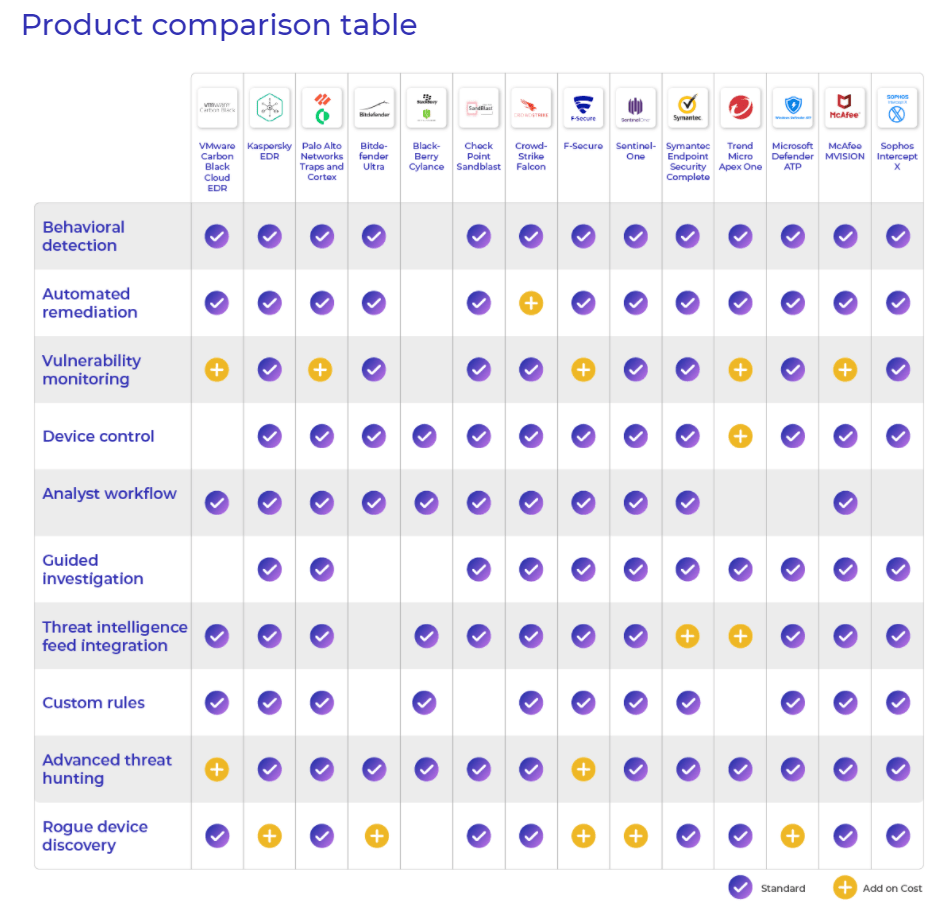
Posted from: https://www.esecurityplanet.com/products/edr-solutions/