Hewlett Packard Enterprise (HPE) has resolved a maximum-severity security flaw in OneView Software that, if successfully exploited, could result in remote code execution.
The critical vulnerability, assigned the CVE identifier CVE-2025-37164, carries a CVSS score of 10.0. HPE OneView is an IT infrastructure management software that streamlines IT operations and controls all systems via a centralized dashboard interface.
“A potential security vulnerability has been identified in Hewlett Packard Enterprise OneView Software. This vulnerability could be exploited, allowing a remote unauthenticated user to perform remote code execution,” HPE said in an advisory issued this week.
It affects all versions of the software prior to version 11.00, which addresses the flaw. The company has also made available a hotfix that can be applied to OneView versions 5.20 through 10.20.
Posted from:
https://thehackernews.com/2026/01/cisa-flags-microsoft-office-and-hpe.html
HPE link:
https://support.hpe.com/hpesc/public/docDisplay?docId=hpesbgn04985en_us&docLocale=en_US
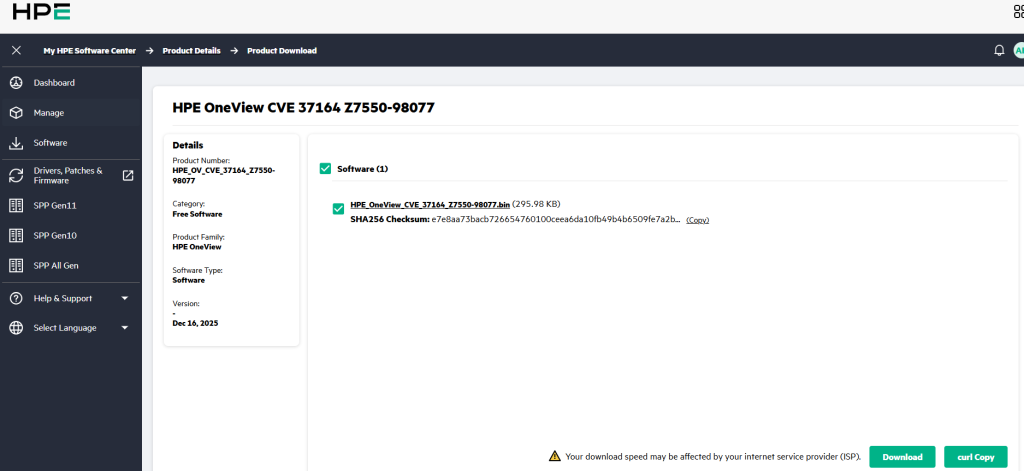
Download page:
https://myenterpriselicense.hpe.com/cwp-ui/product-details/HPE_OV_CVE_37164_Z7550-98077/-/sw_free

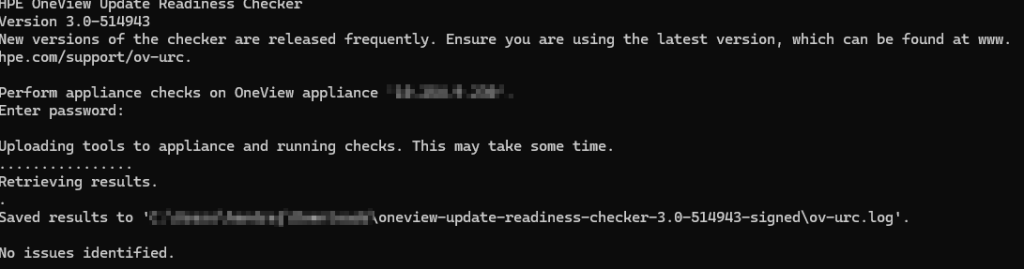
HPE OneView Update Readiness Checker
The HPE OneView Update Readiness Checker is provided for HPE OneView users to evaluate the health of their HPE OneView appliance for a set of known conditions before proceeding with an appliance update. At this point, the checker evaluates conditions only on the appliance and not the managed environment.
https://www.hpe.com/support/ov-urc.
After hotfix update – No issues must be displayed